simo@dev:~$ cat ~/about.md
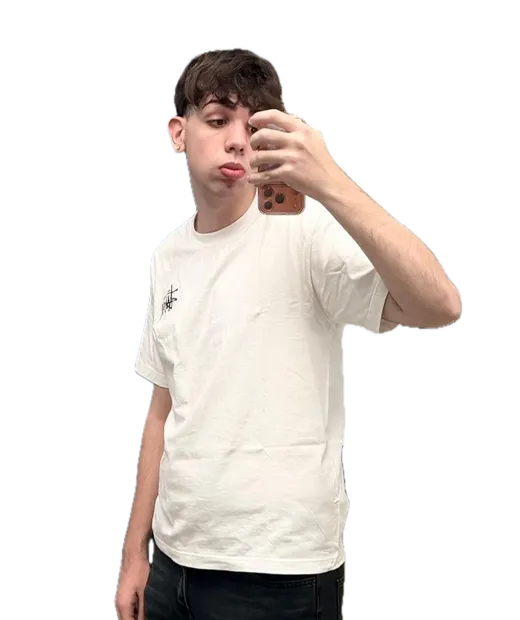
Simone Di Mauro
- Backend Developer
- Security Specialist
- Software Architect
Crafting robust backend systems and securing digital infrastructure. I turn complex problems into elegant, scalable solutions.
I work across the whole path of a backend: REST APIs and data models, the architecture that keeps them maintainable, and the infrastructure they run on, from Linux hosts to DNS, TLS and cloud platforms. Security is part of the design, not a final check: penetration testing, vulnerability assessment and hardening, and automation that keeps those checks in the release pipeline.
Recent work includes Mafdet, a local LLM runner that prefills and reasons while you type, and this site, a static Astro build behind a single Cloudflare Worker with a hardened contact API.
simo@dev:~$ htop --filter=skills --list
-
PID 001
Backend Development
Scalable REST APIs and server architectures. Node.js, Python, Java.
-
PID 002
Database Design
Schema optimization with PostgreSQL, MongoDB, Redis.
-
PID 003
Cybersecurity
Penetration testing, vulnerability assessment, hardening.
-
PID 004
Software Architecture
Maintainable systems using modern design patterns and DDD.
-
PID 005
Cloud Infrastructure
AWS, Azure, GCP — deploy, scale, monitor.
-
PID 006
Security Automation
CI/CD security pipelines and automated threat detection.
simo@dev:~$ cat ./how-i-work.log
-
SSH · srv/linux-core
Linux daily driver
Comfortable with Linux for shell work, processes, permissions, services, logs and terminal-driven automation.
This means faster onboarding on real servers, less operational friction and more autonomy during debugging.
-
DNS · dns-zone.edge
Domains and DNS management
Comfortable working with domains, DNS records, propagation, subdomains, mail routing and connected configurations.
For a company this means connecting apps, websites, email and environments quickly, without getting stuck on infrastructure details.
-
TLS · tls-certificate.chain
TLS, certificates and HTTPS sanity
I pay attention to certificates, HTTPS, redirect hygiene, browser trust warnings and the consistency of the public layer.
That reduces customer-facing issues and improves perceived product reliability from the very first visit.
-
CI · deploy-pipeline.rel
Deploy and release discipline
I care not only about writing code, but also about shipping it through a clean, readable and repeatable release flow.
A company gets less release chaos, clearer handoffs and someone who can contribute to delivery, not just implementation.
-
SYS · logs-monitor.bus
Logs, monitoring and issue hunting
I like reading signals, errors and odd behavior to reconstruct where the flow is actually breaking.
That is extremely useful when real issues need to be understood quickly instead of being approached by blind trial and error.
-
SMTP · mail-delivery.mx
Email delivery and public-facing ops
Familiar with the operational details that keep contact flows, forms, delivery and domain credibility working smoothly.
These are not glamorous topics, but they directly affect leads, support flows and online reputation.
simo@dev:~$ ls /usr/local/bin/*
./programming/
-
 Java
-
 TypeScript
-
 JavaScript
-
 Python
-
 PHP
- SQL and PL/SQL
-
 C
-
 C++
./backend/
-
 Spring Boot (Security, Data JPA, WebSocket)
-
 Node.js
-
 Express
- REST APIs
- OAuth2 and JWT
./frontend/
-
 React
-
 Astro
-
 Next.js
-
 Tailwind CSS
-
 Vite
-
 HTML5
-
 CSS3
-
 Bootstrap
./databases/
-
 MariaDB
-
 MySQL
-
 PostgreSQL
-
 Oracle
-
 Redis
- Drizzle ORM
./devops-cloud/
-
 Docker and Compose
-
 Linux
-
 Nginx
-
 GitHub Actions
-
 Cloudflare Workers
-
 Vercel
-
 Kubernetes (basics)
./security/
- OWASP Top 10 (SQL injection, XSS, CSRF)
- password hashing
- rate limiting
- IP allowlists
- CSP
- Turnstile
./networking/
- MikroTik
- UniFi
- phpIPAM
- DNS
- TLS
./tools/
-
 Git
-
 GitHub
-
 GitLab
-
 IntelliJ IDEA
-
 VS Code
-
 DBeaver
- MySQL Workbench
- Linux
-
 macOS
-
 Windows
$ ls ~/projects
- mafdet/ AI · LLM tooling · 2026
- portfolio/ Web · Infrastructure · 2026
- aryaplus/ Corporate web · 2025
$ ls -t ~/writeups
- Illegal invocation: the Cloudflare Workers bug every test missed
- A contact form endpoint that assumes hostile input